How to Read Security Research News Without Losing the Signal
New security stories can travel faster than the facts behind them. This article shows how to check original sources, match findings to your own systems, and choose a clear next action.
New security stories can travel faster than the facts behind them. This article shows how to check original sources, match findings to your own systems, and choose a clear next action.
cslogwatch is a tool designed to help Cobalt Strike users get handle on the logs generated by the tool. While we can certainly spend our time grepping for data across myriad of beacon session log files, wouldn’t it be nice […]
A few weeks ago I released a blog post titled Stealthy & Targeted Implant Loaders. There are a couple of caveats to the aforementioned points that I would like to address in this brief addendum, in addition to introducing a […]
Implant targeting can be a useful tool in your arsenal; instead of developing weaponized malcode that will execute on arbitrary systems, we can take precautions to protect the confidentiality of our payloads while ensuring deployment occurs only on targeted (intended) […]
A number of researchers have recently been looking at lateral movement methods that leverage Microsoft’s Distributed Component Object Model (DCOM), with some great articles put together by @enigma0x3 at https://enigma0x3.net/. These articles walk through the overall approach of discovering DCOM […]
For those of us that have had the chance to play around with it, docker is pretty awesome. While primarily designed with development / deployment / continuous integration in mind, it is also pretty awesome for offense related tasks. I […]
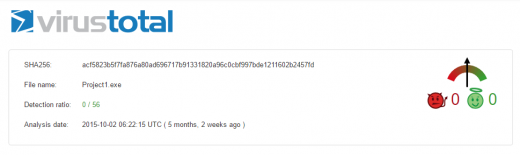
I had originally set out to write a long winded blog post on different antivirus bypass techniques. I went through what was supposed to be step 1 of my guide and uploaded my binary to virustotal… and the binary got […]
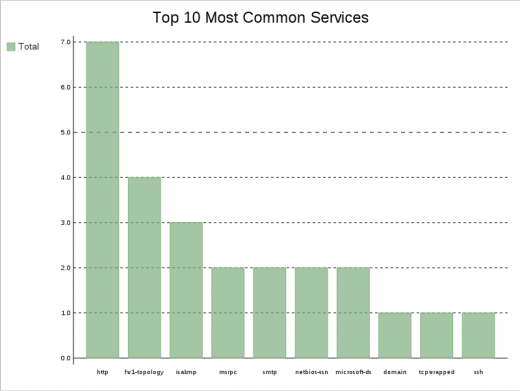
NMAPgrapher can be found at https://github.com/attactics/NMAPgrapher What is it? A tool I created to assist me in providing supplementary data with my penetration test reports. I’m releasing it to the public to do as you wish with it. The primary […]
If you have ever had to conduct a large penetration test, you know just how daunting it can be when you finish port and service scanning and start looking at all the data. While I strongly recommend learning some python […]
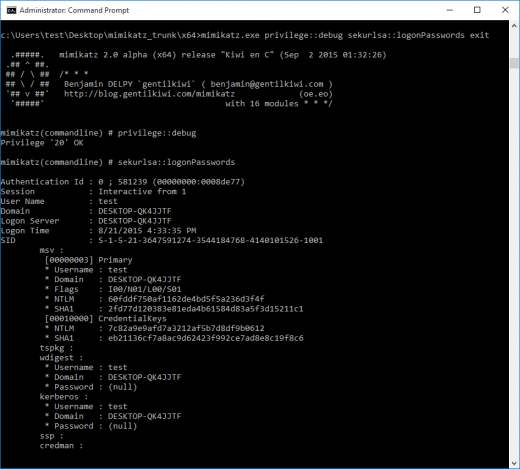
Windows 10 is here. Well… it’s sort of been here for some time, but it’s fully rolled out now and soon we will begin to see enterprise adoption. I, like I’m sure many others out there, have been playing with […]
So, you’ve pwned all the things, you have the keys to the kingdom, and you’ve pilfered all the data. You’ve done a great job, and now you’re done right? Wrong. I’ve been working in the offensive side of the infosec […]